Home / Commercial
From exposed asset to affected business service to fix
Show which business services an exposure reaches, send the fix to an owner, and keep the evidence your auditors ask for.
Business-service exposure
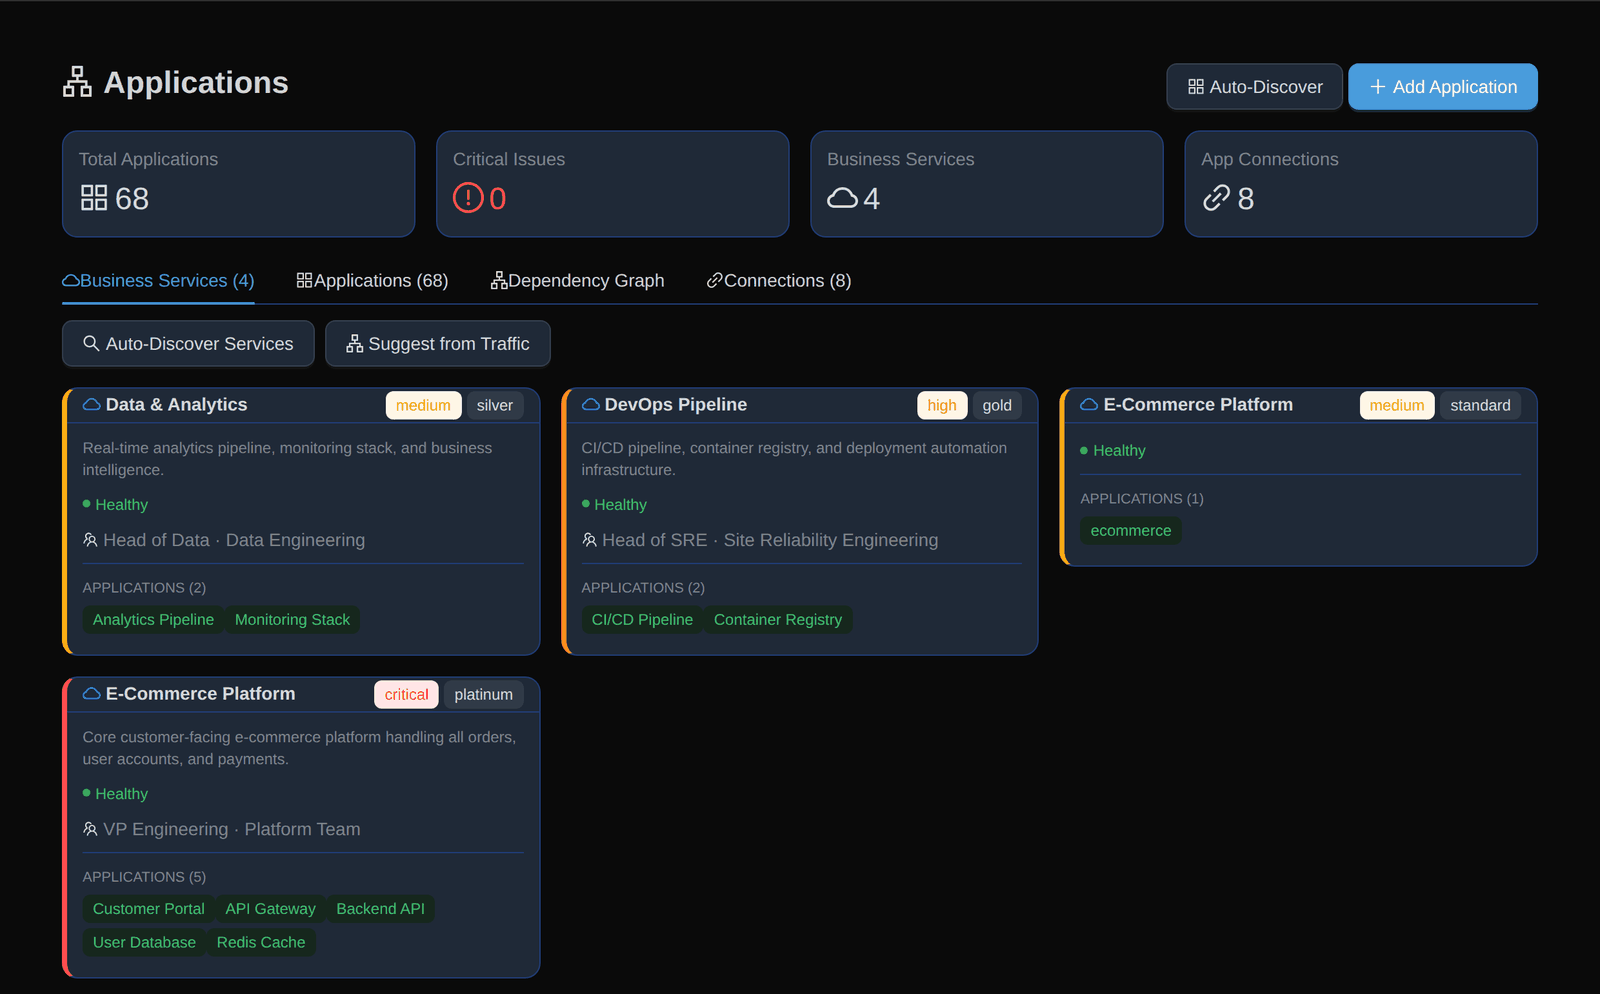
Findings are more useful when they name what is at stake. Infracast follows an attack path from an internet-facing asset to the data at its end and shows the assets and data classification along the way.
Attack paths account for network egress, gateways and security groups. Applications are grouped into Business Services, each with a criticality, an SLA tier, an owner and a team, so the owner and the impact are visible in one place.
Remediation workflow
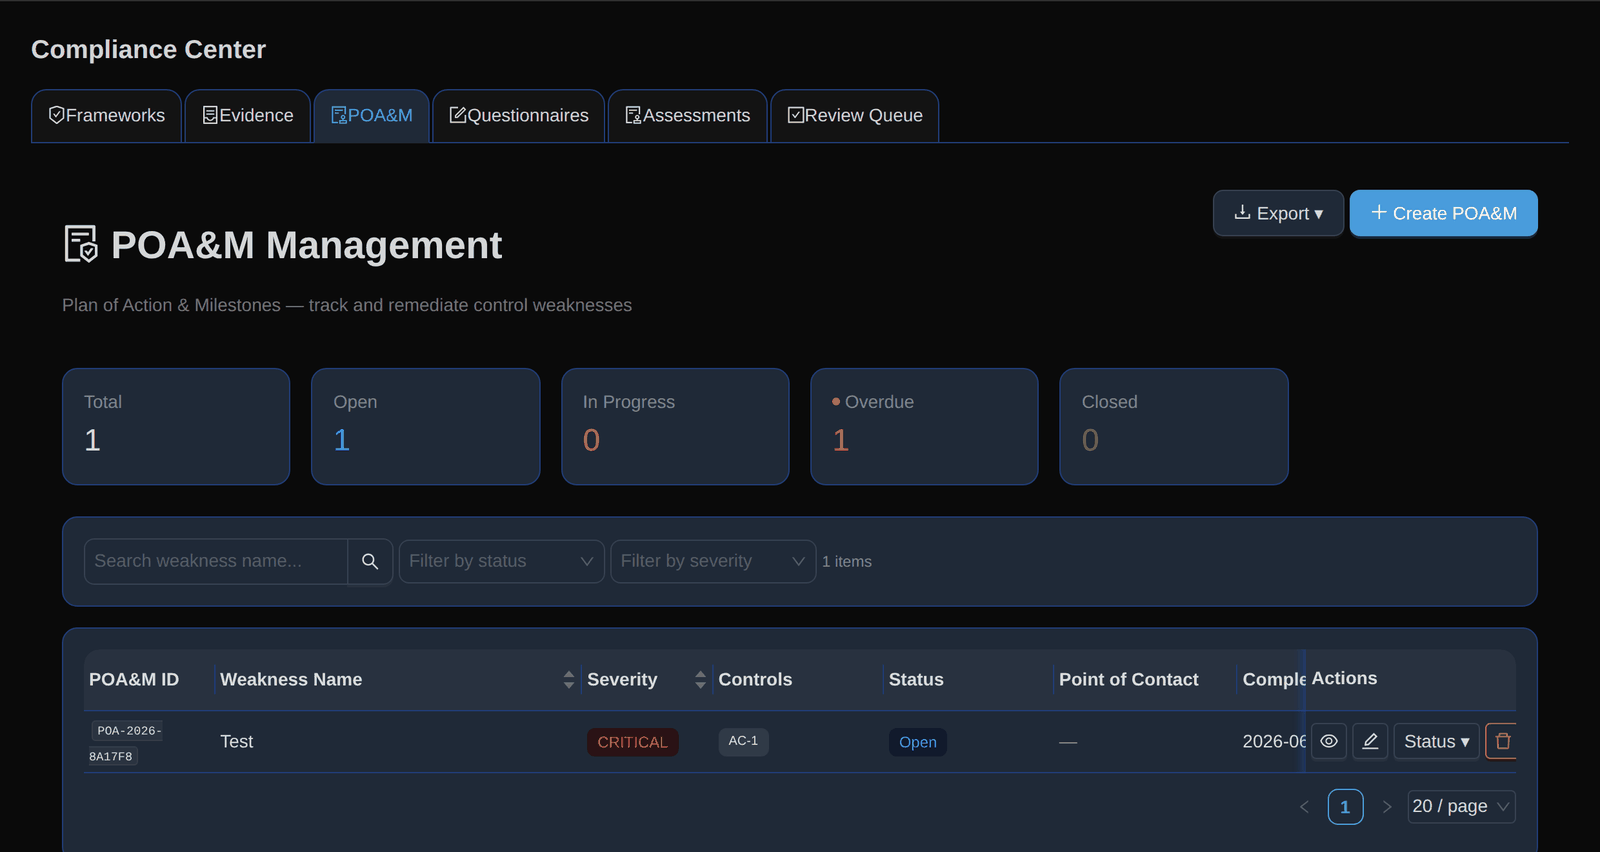
Track each weakness as a POA&M item (Plan of Action and Milestones) with severity, mapped controls, status, a point of contact and a scheduled completion date, so the work is visible in the same place as the evidence.
Findings that cannot be fixed right away can be accepted as a risk rather than dropped from view.
Evidence
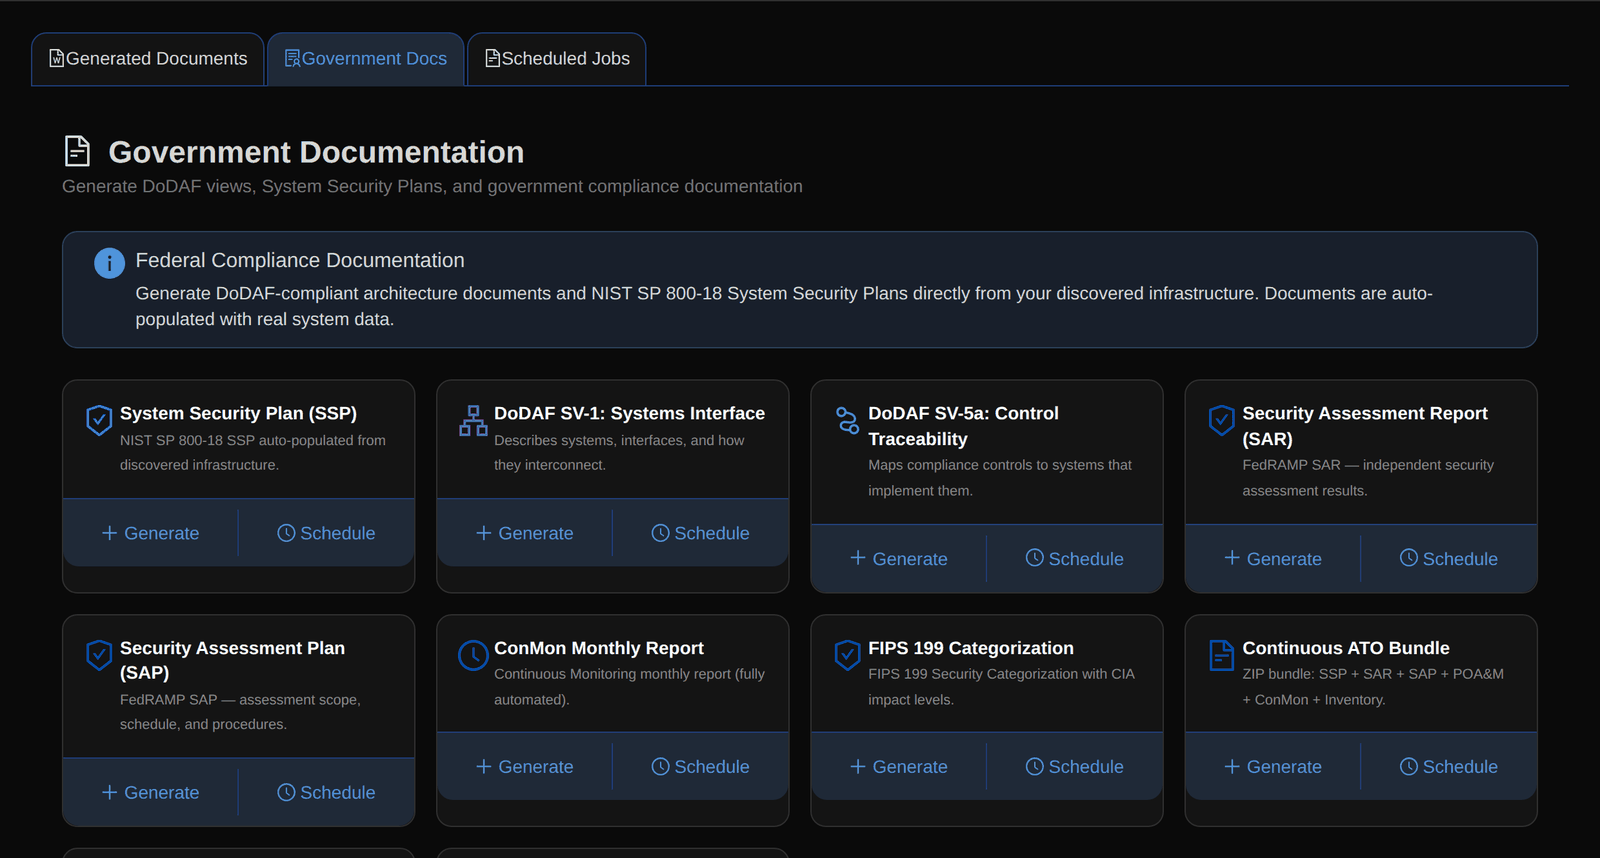
Evidence is collected from the environment as part of normal scans and kept with the asset and the control it supports. Reports and questionnaire drafts are built from it. People review and approve before anything goes to an auditor or customer.
Examples
Healthcare
Scope the infrastructure that touches ePHI
For HIPAA work, start by finding the systems that store or process ePHI. Infracast shows which assets sit on attack paths to data classified as sensitive, so scoping and risk analysis start from the environment as it is.
Framework content: HIPAA (healthcare pack).
Infracast supports your risk analysis; it does not make you HIPAA compliant.
Financial services
Evidence for PCI DSS and SOC 2
Keep an inventory of in-scope systems, the findings against them and the evidence for each requirement in one place, ready for your assessor or auditor to review.
Framework content: PCI DSS and SOC 2 (financial services pack).
Your assessor decides what satisfies a requirement.
See it on your own questions
Look at the sample-data demo, run a 14-day trial, or ask for a technical walkthrough with an engineer.